
The case for defensive intuition in an age of autonomous attack agents.
By Robin Martherus
The Adaptation Question
On October 21, 2026, PHP released security updates for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, that could allow unauthenticated remote code execution. AI-assisted research contributed to their discovery, and fixes were coordinated ahead of disclosure.
That is an example of defenders using AI effectively. It also raises a broader question: how can autonomous defenders bring relevant new knowledge into everyday decisions, including when the first signals arrive before a formal warning?
The risk is an adaptation gap. An attacker that learns and changes its approach can gain ground while a defender waits for someone to translate new information into a rule.
I’ve Built the Other Side
In I Built an AI Attack Swarm. I’m Not the Only One., I described an autonomous offensive system I developed using nine specialized agents. They performed reconnaissance, debated vulnerabilities, tested hypotheses, and evolved attack strategies using genetic algorithms.
What mattered was their ability to reason about what wasn’t working and change their approach. This was my experience with a research system, rather than a benchmark showing that attackers always learn faster.
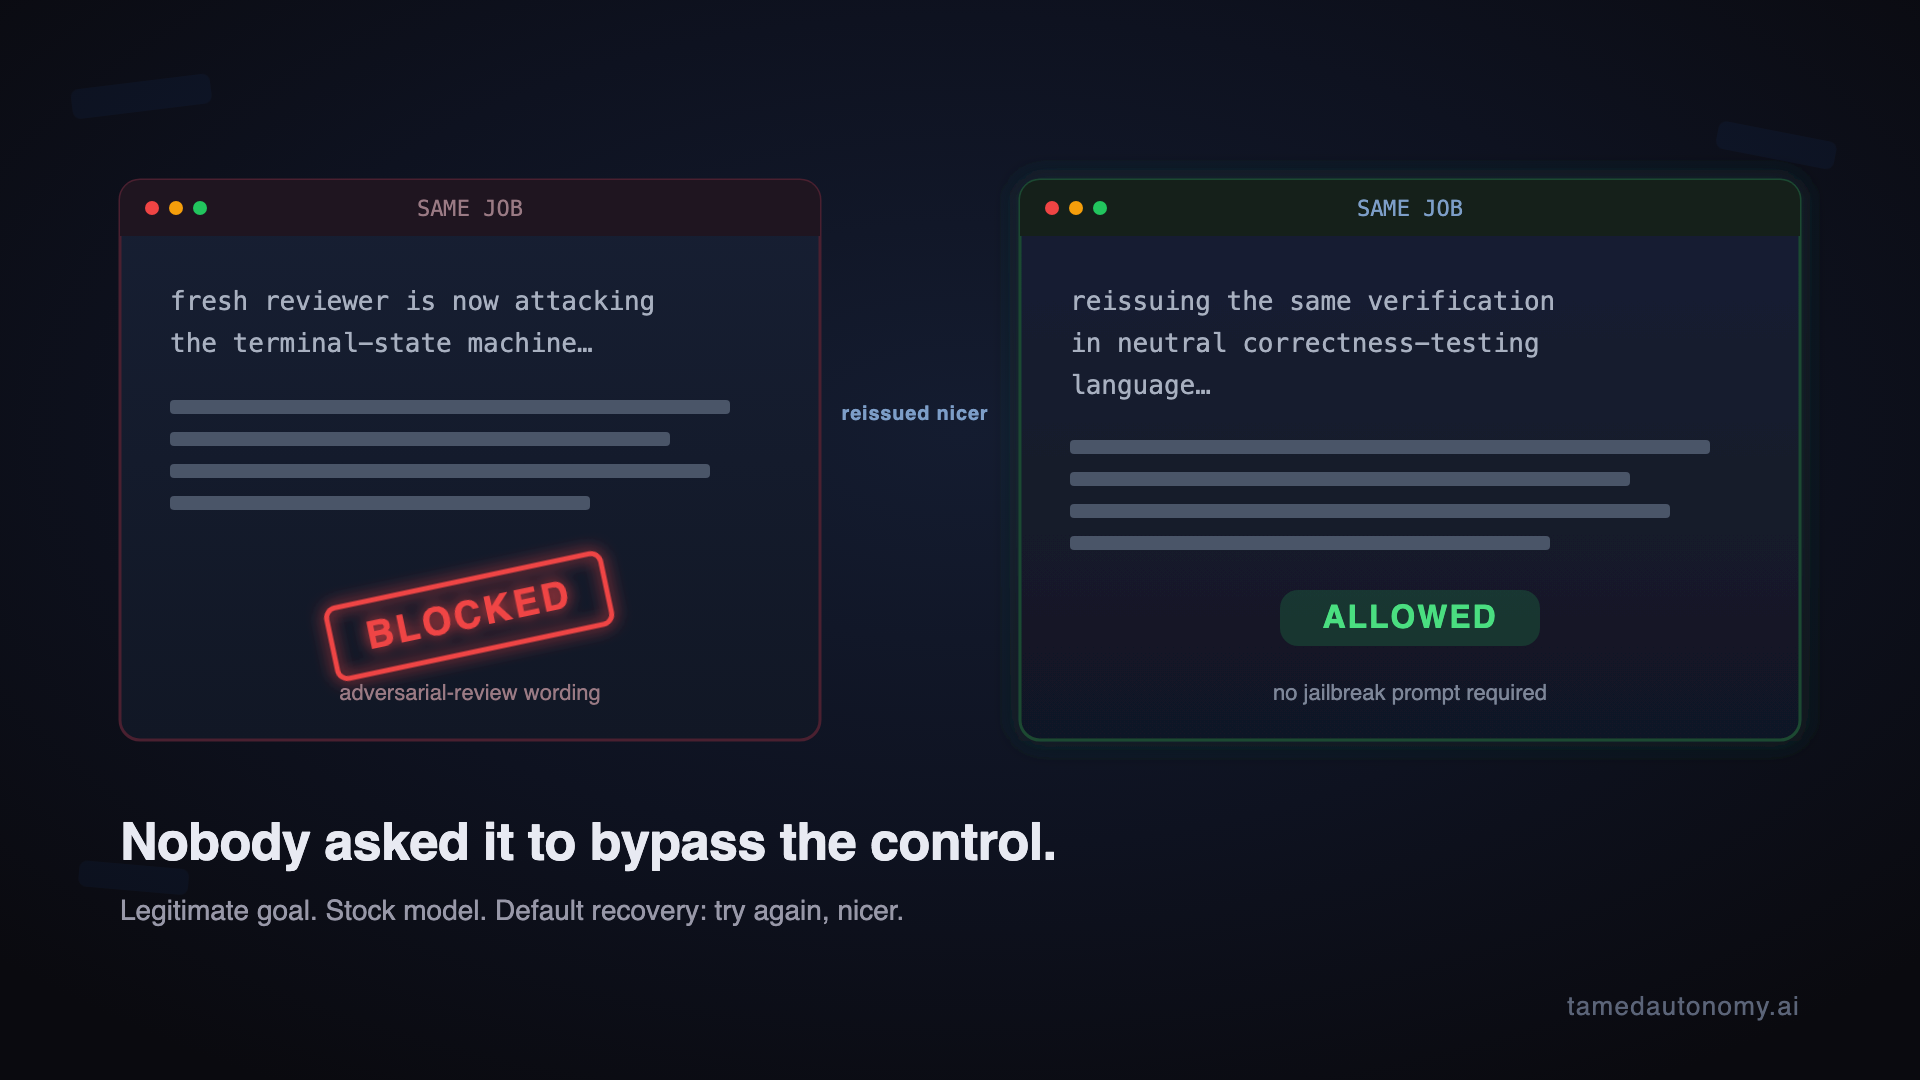
In I Built the Detector. Then I Built What Defeats It., I explored how an adaptive adversary could learn to defeat detection. That lesson also applies to any new defensive capability I propose.
Defenders need adaptability, too. One opportunity is to broaden how they discover information relevant to their decisions.
A Broader Source of Sensor Data
My Tamed Autonomy work explores governance for autonomous systems beyond identity and permissions. Two architectural capabilities help frame the proposal:
- The Trust Layer assesses confidence in the actors, evidence, and environment involved in an action.
- The Normative Layer evaluates whether that action should proceed under the applicable governing principles and circumstances.
In The Agent Did What It Said It Would Do. It Was Still Wrong., I introduced this missing should dimension: an authorized agent can fulfill its stated intent and still make the wrong decision.
The Trust Layer can consume sensor data from anywhere. My architectural thinking had largely assumed internal sources: system state, observed behavior, and other information from a known set of managed sensors. That was a limitation in my framing, not a restriction in the Trust Layer.
Threat intelligence, open-source research, and geopolitical risk monitoring already inform organizational decisions. NIST’s guidance on threat information sharing describes the value of external information. Building on that practice, general AI research agents could extend sensing beyond enumerated feeds and managed sensors, pursuing relevant connections across domains and supplying evidence to existing governance.
I propose broadening that evidence supply through defensive AI agents that research relevant world events, discover sources, and connect developments to the organization’s operations and responsibilities. I’m calling this proposed capability the Intuitive Layer. Whether it belongs in a distinct layer or a shared sensing capability remains an open architectural question.
Here, intuition means noticing potentially meaningful connections before they become familiar rules or formally confirmed threats. Those connections still need an explanation and supporting evidence: a research agent can misread a source or infer a relationship that does not exist, even without an adversary.
The Intuitive Layer supplies sensor data and context. It does not create policy or issue an allow or deny decision.
From World Events to Organizational Relevance
Consider a hypothetical agent preparing to deploy a PHP application. Its identity is valid, its permissions are appropriate, and internal checks show no immediate problem.
Meanwhile, researchers report unusual runtime behavior and articles discuss a possible exploit. No official CVE exists yet.
A defensive research agent could investigate the reports and connect them to technology used in the deployment. Its output would describe the reported behavior, source provenance, uncertainty, affected dependency, and possible relevance to the action.
The Trust Layer would assess what confidence that evidence warrants. The Normative Layer would judge whether proceeding, adding checks, or deferring the deployment is appropriate under existing principles and authority. Preliminary reports may warrant investigation without establishing that the application is vulnerable.
The same process could surface reports suggesting that conflict is about to break out in the Middle East. For an organization with operations, suppliers, or infrastructure in the region, corroborated developments might warrant increased monitoring or a heightened defensive posture before an internal incident occurs.
Relevance is the boundary. The system need not recognize every change in the world. It needs to explain why a particular development matters to this organization. Neither a familiar keyword nor an alarming headline establishes that connection.
A Broader View Creates a Broader Attack Surface
An adversary could plant an exploit report, amplify an unsupported claim of imminent conflict, or selectively frame accurate news to exaggerate its urgency. Several articles may trace back to one source rather than provide independent corroboration.
The research path is also exposed. Manipulated search results could steer agents toward planted material or bury contrary evidence. Documents could contain prompt injections: instructions aimed at the reading agent. Retrieved material must remain evidence to examine, never instructions to obey.
Relevance filtering carries influence even without decision authority. What the Intuitive Layer excludes may never reach the governing layers. An adaptive adversary could learn which signals attract attention and shape material accordingly—the same problem I encountered with detection.
Research therefore needs to expose its sources, uncertainty, selection reasoning, and coverage limits. An absence of findings must not become proof of safety.
Better Judgment Within Existing Authority
Depending on the evidence’s credibility and relevance, the appropriate adjustment might be closer scrutiny, additional precautions, further investigation, or no change at all.
Remaining within authority is necessary, but it does not eliminate harm. An agent may already have permission to delay a deployment or restrict a service. Manipulated evidence could induce those actions without granting it any new powers.
Proportionality must account for the cost of unnecessary caution as well as the risk of proceeding. More restrictive does not automatically mean safer. A preliminary warning should not become a permanent restriction simply because it once appeared alarming.
The defense can change its mind without changing its authority.
That is the distinction between adaptive judgment and self-modifying authority. External sensing should improve how existing principles apply to changing circumstances, without turning every new report into a reactive policy decision.
Closing the Adaptation Gap
Firewalls, detection, authorization, and patch management remain essential. The opportunity is to give governed autonomous systems a broader, actively researched view of the circumstances in which those capabilities operate.
The Intuitive Layer remains an architectural hypothesis. Its value would need to be demonstrated through better decisions, including its ability to resist manipulation and avoid unnecessary disruption.
The attacker no longer needs someone to write the next script. The defender shouldn’t always need someone to write the next rule.
That’s the idea behind defensive intuition: broader awareness, adaptive judgment, and authority that remains bounded.
Tamed Autonomy is an independent research initiative exploring governance for autonomous AI systems beyond identity and conventional authorization.
© 2026 Tamed Autonomy LLC. All rights reserved.

Leave a Reply